
Scope creep ends here.
Treaty is scope intelligence for service businesses. Track client commitments, review scope changes before extra work begins, and connect approved changes to commercial follow-through.
Agencies
Consultancies
Studios
Service teams
Good projects lose margin quietly.
Scope drift rarely arrives as a formal change request. It appears through calls, messages, and “small” additions that have no shared commercial record.
Unrecorded extra work
Additional requests become expected delivery when the team has no consistent change process.
Promises without ownership
Commitments remain spread across messages, meetings, and individual memory.
Approved work not invoiced
Commercial decisions lose their connection to billing and revenue follow-through.
One workspace for the commercial truth.
Treaty connects project delivery, commitments, scope decisions, invoices, and audit history instead of treating them as separate administrative tasks.
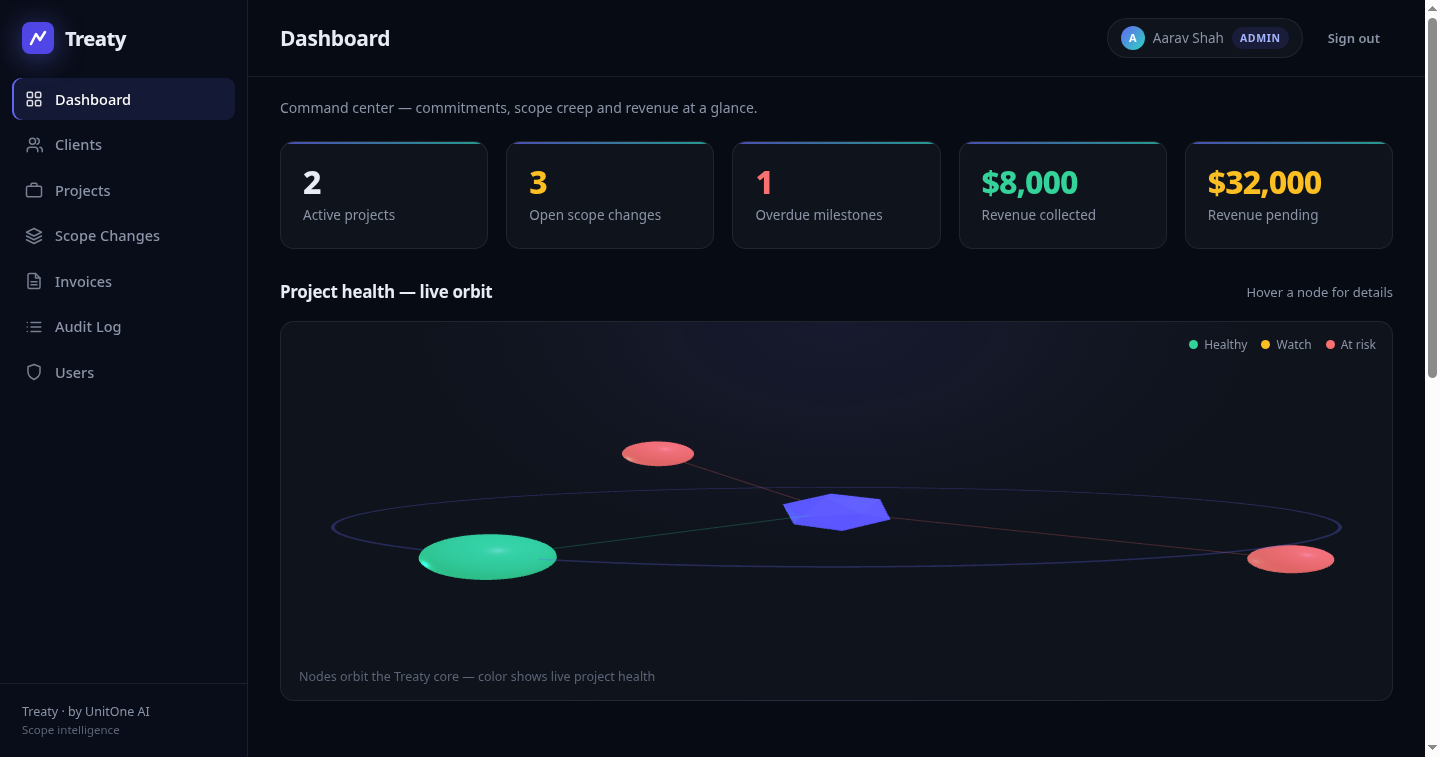
Projects & milestones
Define the work sold, its delivery stages, owners, and deadlines in one shared record.
Commitment tracking
Turn client promises into owned commitments with due dates and visible delivery status.
Scope-change decisions
Propose, review, approve, or reject changes before additional work quietly becomes expected work.
Invoices & follow-through
Connect approved commercial changes to draft, sent, paid, and overdue invoice states.
Append-only audit history
Record mutations and approvals with the responsible user and supporting context.
Role-based access
Separate member workflows from administrative approvals, billing, user management, and audit access.
Make change visible before work proceeds.
Define what was agreed
Record the client, project, milestones, and commitments that form the delivery baseline.
Review what changed
Propose the request with budget or timeline impact, then capture the decision in the open.
Follow through commercially
Keep approved changes connected to invoices, payment status, and an attributable audit trail.
Practical controls around sensitive commercial records.
Treaty can run as a single container on private infrastructure. Access, validation, rate limiting, and audit controls are enforced by the application—not left to interface convention.
Discuss security requirements- bcrypt password hashing with httpOnly session cookies
- Helmet security headers and a restrictive Content Security Policy
- Rate-limited APIs with stricter protection on authentication
- Schema-validated input and parameterized database queries
- Role enforcement for approvals, billing, users, and audit access
- Docker or private VPS deployment with customer-controlled storage
Bring scope and commercial decisions into one accountable workflow.
Request a walkthrough using a representative project, or discuss a private pilot for one delivery team.
Request a Treaty pilot